DevSecOpsNow Delivers Resilient Cloud Native Security Automation For Engineering Teams
Introduction
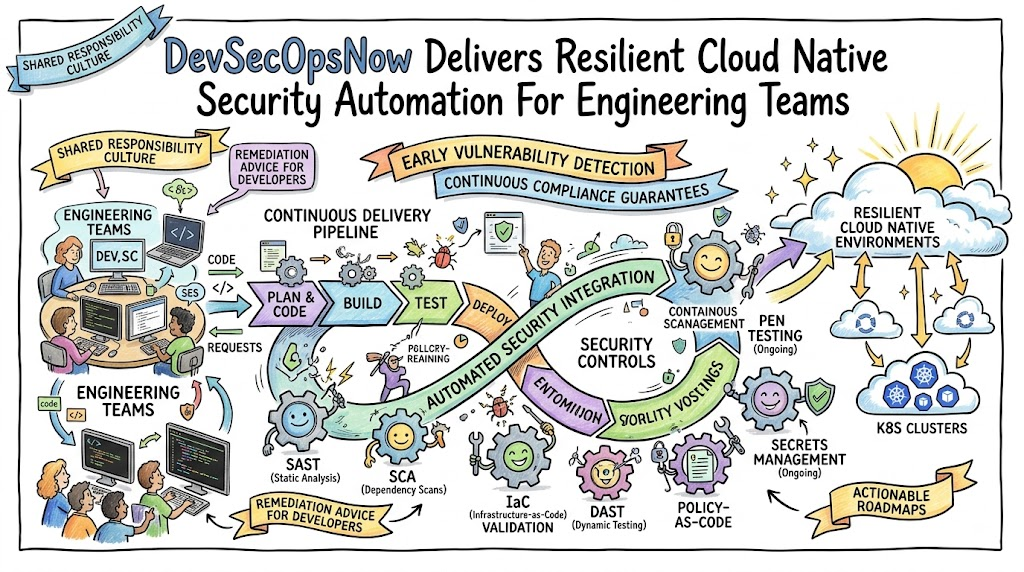
Modern software delivery demands speed, yet rapid deployments frequently introduce critical vulnerabilities into production environments. Engineering teams often push features quickly, while traditional security teams struggle to catch up before release deadlines. Consequently, unpatched packages, loose permissions, and misconfigured infrastructure assets expose digital platforms to malicious threats.DevSecOpsNow bridges this gap by shifting security controls directly into continuous delivery pipelines. Therefore, developers resolve defects instantly during coding cycles rather than handling expensive incidents later. By unifying people, automated testing frameworks, and cloud controls, modern organizations protect their entire digital ecosystem while increasing software delivery velocity.
What Is DevSecOpsnow?
DevSecOpsNow operates as a specialized platform and advisory partner dedicated to embedding automated security into contemporary DevOps engineering environments. The initiative empowers development, operations, and security practitioners to collaborate under shared guardrails and unified delivery metrics.Instead of positioning security as an isolated approval gate, DevSecOpsNow embeds automated analysis across code repositories, build systems, container platforms, and live clouds. As a result, engineering groups maintain total visibility over their risk posture while shipping business value rapidly every single day.
Why DevSecOps Matters
Traditional security audits occur at the tail end of delivery cycles, causing massive release delays and team friction. Moreover, fixing an architectural flaw or vulnerability in production costs up to thirty times more than resolving it during development.
+-----------------------------------------------------------------------------------+
|                            TRADITIONAL VS MODERN DEVSECOPS                        |
+--------------------------+----------------------------+---------------------------+
| Dimension                | Traditional Security       | Modern DevSecOps          |
+--------------------------+----------------------------+---------------------------+
| Security Review Stage    | Pre-production manual gate | Continuous automated runs |
| Developer Feedback Loop  | Weeks or months later      | Instant (within minutes)  |
| Remediation Responsibility| Isolated security team    | Shared engineering teams  |
| Deployment Velocity      | Slow and unpredictable     | Rapid, secure, and steady |
+--------------------------+----------------------------+---------------------------+
When teams adopt security automation early, vulnerability counts drop by more than fifty percent across initial build cycles. Furthermore, automated policy enforcement guarantees regulatory compliance without requiring tedious manual documentation audits before every deployment.
Core Building Blocks of a DevSecOps Program
A sustainable engineering program relies on three interconnected pillars, namely automated tooling, standardized workflows, and continuous organizational governance.
+-----------------------------------------------------------------------------------+
|                         CORE PILLARS & ESSENTIAL TOOLING                          |
+-------------------------+----------------------------------+----------------------+
| Core Capability         | Key Operational Objectives       | Representative Tools |
+-------------------------+----------------------------------+----------------------+
| Static Analysis (SAST)  | Catch insecure code patterns     | SonarQube, Semgrep   |
| Dependency Check (SCA)  | Eliminate vulnerable libraries   | Snyk, Trivy          |
| Dynamic Testing (DAST)  | Detect runtime vulnerabilities   | OWASP ZAP, Burp Suite|
| Infrastructure as Code  | Block cloud misconfigurations    | Checkov, tfsec       |
| Secret Detection        | Prevent leaked credentials       | GitGuardian, TruffleH|
+-------------------------+----------------------------------+----------------------+
First, integrate automated scanners directly into pull request checks so developers receive actionable remediation guidance instantly. Next, establish clear vulnerability classification matrices to eliminate confusion regarding severity levels and resolution deadlines. Finally, track key delivery metrics such as mean time to remediate and build failure rates to maintain continuous operational improvement.
DevSecOps and Cloud Security
Modern cloud infrastructure moves dynamically through code, requiring teams to secure configurations long before deploying assets. Cloud Security Consulting Services help organizations protect multi-cloud architectures across identity configurations, runtime workloads, and data storage boundaries.Furthermore, engineering teams must validate Terraform, OpenTofu, and CloudFormation templates using automated policy-as-code engines. Consequently, infrastructure engineers block exposed storage buckets and open network routes before cloud resources initialize. Dedicated Kubernetes Security Consulting Services reinforce container environments by enforcing admission controllers, mutual TLS communication, and granular role-based access policies.
Software Supply Chain Security
Open-source libraries constitute over eighty percent of modern enterprise codebases, creating significant exposure to upstream compromises and malicious packages. Therefore, organizations need specialized Software Supply Chain Security Services to secure external code dependencies, base images, and build pipelines.Engineering teams must generate verifiable Software Bills of Materials for every release artifact across the pipeline. In addition, implementing cryptographic artifact signing with tools like Cosign verifies build provenance and protects container registries against tampering. By maintaining strict control over external dependencies, companies prevent upstream library compromises from impacting production systems.
Security Testing Across the SDLC
Embedding continuous verification throughout software lifecycles requires layered testing techniques rather than relying on a single scanning tool.
- Code and Commit Phase: Developers scan source code using pre-commit hooks and real-time IDE plugins to capture insecure syntax.
- Build and Packaging Phase: Automated pipelines execute software composition analysis and container image scanning to block vulnerable packages.
- Staging and Testing Phase: Dedicated runners launch automated dynamic scans and API security checks against running environments.
- Runtime Verification: Comprehensive Penetration Testing Services uncover exploitable architectural weaknesses across networks, APIs, and microservices before malicious attackers discover them.
DevSecOps Assessment: Finding the Starting Point
Organizations frequently struggle to determine where to begin their security modernization journeys. Professional DevSecOps Assessment Services evaluate current development workflows, operational maturity, and tooling coverage against industry benchmarks.During an assessment, specialists analyze continuous delivery pipelines, access control models, and incident remediation timelines across all engineering units. Subsequently, leaders receive a structured maturity roadmap that prioritizes high-risk vulnerabilities and outlines practical implementation milestones. This diagnostic baseline ensures that subsequent tooling investments directly address real security risks.
DevSecOps Consulting Services
Navigating complex regulatory requirements while maintaining engineering agility requires specialized strategic guidance. Tailored DevSecOps Consulting Services enable businesses to design resilient delivery architectures, establish zero-trust security postures, and build scalable automated pipelines.Consultants collaborate closely with engineering leaders to define custom security gates, evaluate enterprise tools, and establish governance frameworks. Additionally, this advisory support aligns security strategies with business goals, ensuring technology investments enhance engineering speed rather than creating bureaucratic friction.
DevSecOps Implementation Services
Adopting security tooling often causes noisy alerts and developer frustration when configurations lack proper pipeline tuning. Hands-on DevSecOps Implementation Services integrate Static Application Security Testing, dynamic analyzers, and secret scanners directly into Git platforms and delivery orchestrators.Engineers configure automated quality gates that break builds only for critical, exploitable vulnerabilities, keeping developer workflows smooth. Furthermore, specialists build automated vulnerability management dashboards that centralize findings and assign tickets automatically to responsible engineers. This operational structure transforms security from a theoretical goal into an automated reality.
DevSecOps Managed Services
Many organizations face persistent shortages of qualified security automation professionals to manage daily operations. Dedicated DevSecOps Managed Services deliver round-the-clock security engineering support, pipeline maintenance, policy tuning, and proactive vulnerability triage.Managed specialists continuously monitor pipeline scan outcomes, validate genuine risks, and eliminate noisy false positives for developers. Moreover, the team updates scanning rules and cloud security policies whenever new threat vectors emerge across the software industry. This ongoing support ensures consistent enterprise protection without overloading internal development teams.
DevSecOps Training for Professionals
Individual practitioners need practical skills to navigate modern continuous integration and container security ecosystems effectively. Immersive DevSecOps Training courses provide engineers with hands-on experience in writing secure code, configuring scanners, and hardening cloud environments.Participants gain direct practice securing container registries, configuring runtime policies with Falco, and securing infrastructure deployments. Consequently, developers and DevOps practitioners expand their technical capabilities, making them valuable contributors to modern cloud native engineering teams.
Corporate DevSecOps Training
Transforming organizational security posture requires collective alignment across development, infrastructure, quality assurance, and security teams. Comprehensive Corporate DevSecOps Training programs upskill enterprise engineering departments through customized, interactive laboratory environments.
+-----------------------------------------------------------------------------------+
|                        ENTERPRISE TEAM TRAINING MATRIX                            |
+----------------------+---------------------------------+--------------------------+
| Engineering Role     | Primary Learning Objectives     | Core Hands-On Labs       |
+----------------------+---------------------------------+--------------------------+
| Software Developers  | Secure coding, SAST, SCA triage | IDE tools, pull requests |
| DevOps Engineers     | Pipeline security, secret mgmt  | CI/CD gates, vault setup |
| Cloud Engineers      | Cloud posture, IaC policy code  | Terraform, admission ctrl|
| Security Analysts    | Threat modeling, vulnerability  | Centralized triage, DAST |
+----------------------+---------------------------------+--------------------------+
These programs simulate real-world security incidents and pipeline failures, training engineers to resolve vulnerabilities efficiently without stalling production releases. As a result, cross-functional teams establish shared operational vocabulary and collaborate seamlessly on everyday security challenges.
Common DevSecOps Mistakes
Organizations often make critical errors when rushing into automated pipeline security without strategic planning.First, turning on all scanning rules simultaneously floods developers with thousands of low-priority alerts. This mistake causes alert fatigue, leading developers to bypass or ignore security warnings entirely.Second, teams frequently purchase expensive security software without training their developers on remediation practices. Without proper coaching, security backlogs continue to grow despite high tool expenditures. Finally, treating security as an isolated toolchain rather than an engineering discipline inevitably recreates the organizational silos that DevSecOps is meant to eliminate.
How to Build a Sustainable DevSecOps Culture
Sustained engineering success depends heavily on cultural collaboration, mutual empathy, and shared responsibility. Organizations must introduce Security Champions programs, placing trained developers within individual product squads to offer peer guidance.
+-----------------------------------------------------------------------------------+
|                      CULTURAL MATURITY EVOLUTION TIMELINE                         |
+---------------------+-------------------------------+-----------------------------+
| Cultural Phase      | Key Operational Behaviors     | Primary Milestone Outcome   |
+---------------------+-------------------------------+-----------------------------+
| Phase 1: Awareness  | Baseline security education   | Security champions selected |
| Phase 2: Automation | CI/CD testing integration     | Automated pull request scans|
| Phase 3: Ownership  | Squads manage triage backlogs | Low MTTR and minimal friction|
+---------------------+-------------------------------+-----------------------------+
Furthermore, leaders should reward teams that maintain low remediation times and resolve vulnerabilities proactively. When security metrics celebrate developer enablement rather than placing blame for defects, teams embrace security practices willingly.
DevSecOpsNow as a Practical Resource
DevSecOpsNow functions as a dedicated partner for enterprises modernizing their software delivery and security architecture. By combining consulting, managed operations, and hands-on corporate education, the platform solves security challenges for modern engineering teams.Whether an organization needs an initial maturity assessment, managed Kubernetes protection, or customized pipeline integration, DevSecOpsNow provides practical technical guidance. This comprehensive support model allows businesses to deploy cloud applications with confidence.
A Practical DevSecOps Roadmap
Executing a smooth transition toward automated pipeline security requires a structured step-by-step approach.
+-----------------------------------------------------------------------------------+
|                        STEP-BY-STEP ADOPTION BLUEPRINT                            |
+-------------------+-----------------------------------+---------------------------+
| Execution Step    | Tactical Implementation Tasks     | Deliverable / Artifact    |
+-------------------+-----------------------------------+---------------------------+
| Step 1: Discover  | Map software supply chains        | Complete tool & asset map |
| Step 2: Integrate | Embed SAST, SCA in pull requests  | Automated scan pipelines  |
| Step 3: Hardening | Enforce IaC rules & policy engines| Compliant cloud templates |
| Step 4: Governance| Deploy runtime monitors & metrics | Unified risk dashboards   |
+-------------------+-----------------------------------+---------------------------+
First, catalog all source repositories, cloud infrastructure resources, and continuous integration pipelines across the organization. Next, implement automated static analysis and dependency scanning for all critical microservices.Following pipeline automation, enforce infrastructure-as-code security policies and runtime admission controls across cloud clusters. Finally, establish automated dashboards to track vulnerability resolution speeds and maintain governance standards continuously.
Frequently Asked Questions About DevSecOpsNow
What primary services does DevSecOpsNow provide to engineering teams?DevSecOpsNow provides end-to-end consulting, automated pipeline implementation, managed operations, cloud and Kubernetes security, supply chain hardening, penetration testing, and corporate training programs.How do automated security gates prevent software release delays?Automated gates scan code changes during pull requests, allowing developers to detect and fix defects in minutes without waiting for manual security reviews before deployment.Why is software composition analysis essential for modern applications?Software composition analysis scans third-party open-source libraries within codebases, identifying known vulnerabilities and outdated dependencies before bad actors can compromise running systems.What is the main benefit of policy-as-code in cloud environments?Policy-as-code validates infrastructure templates automatically, preventing insecure configurations such as open network ports and unencrypted databases from provisioning in live environments.How does corporate training improve organizational security posture?Corporate training provides developers and operations engineers with hands-on practice in identifying risks, tuning scanners, and fixing vulnerabilities directly within everyday continuous integration workflows.What is the difference between static and dynamic application security testing?Static testing analyzes application source code for flaws without executing the program, whereas dynamic testing evaluates running applications from the outside to uncover active runtime weaknesses.Why are penetration testing services necessary alongside automated scanners?Penetration testing simulates real-world manual attack techniques, uncovering complex business logic flaws and multi-step exploitation paths that automated vulnerability scanners cannot detect.How do managed services support organizations facing security talent shortages?Managed services provide dedicated external engineers who handle tool maintenance, continuous alert triage, policy updates, and remediation guidance, allowing internal teams to focus on core product features.What role do security champions play in engineering departments?Security champions act as embedded security advocates within development squads, guiding teammates on secure coding practices and helping resolve vulnerability backlogs quickly.How does an initial assessment accelerate pipeline security maturity?An initial assessment identifies existing workflow gaps, evaluates tooling coverage, and creates a prioritized roadmap, ensuring organizations invest resources where they provide the greatest security value.
Final Thoughts
Modern software delivery moves quickly, making manual security approvals impractical for scalable engineering operations. Organizations that embed security automation directly into continuous integration workflows protect their assets while maintaining high release velocity.By combining continuous pipeline scanning, cloud hardening, supply chain verification, and hands-on team education, businesses build resilient architectures. Partnering with experienced specialists and adopting practical operational frameworks ensures your engineering teams deliver secure, high-performance software with complete confidence.
